
Everything from code to production, in one platform
Six areas, from the first line of code to production, on AWS, Google Cloud and Azure. Each capability removes a specific wait — open one for the detail.
Develop & preview
A running app before the first ticket
Sketch the stack, run it on your laptop, and get a private live link for every branch. Nobody waits for a shared staging server.
Build & test
Every build checked before it moves on
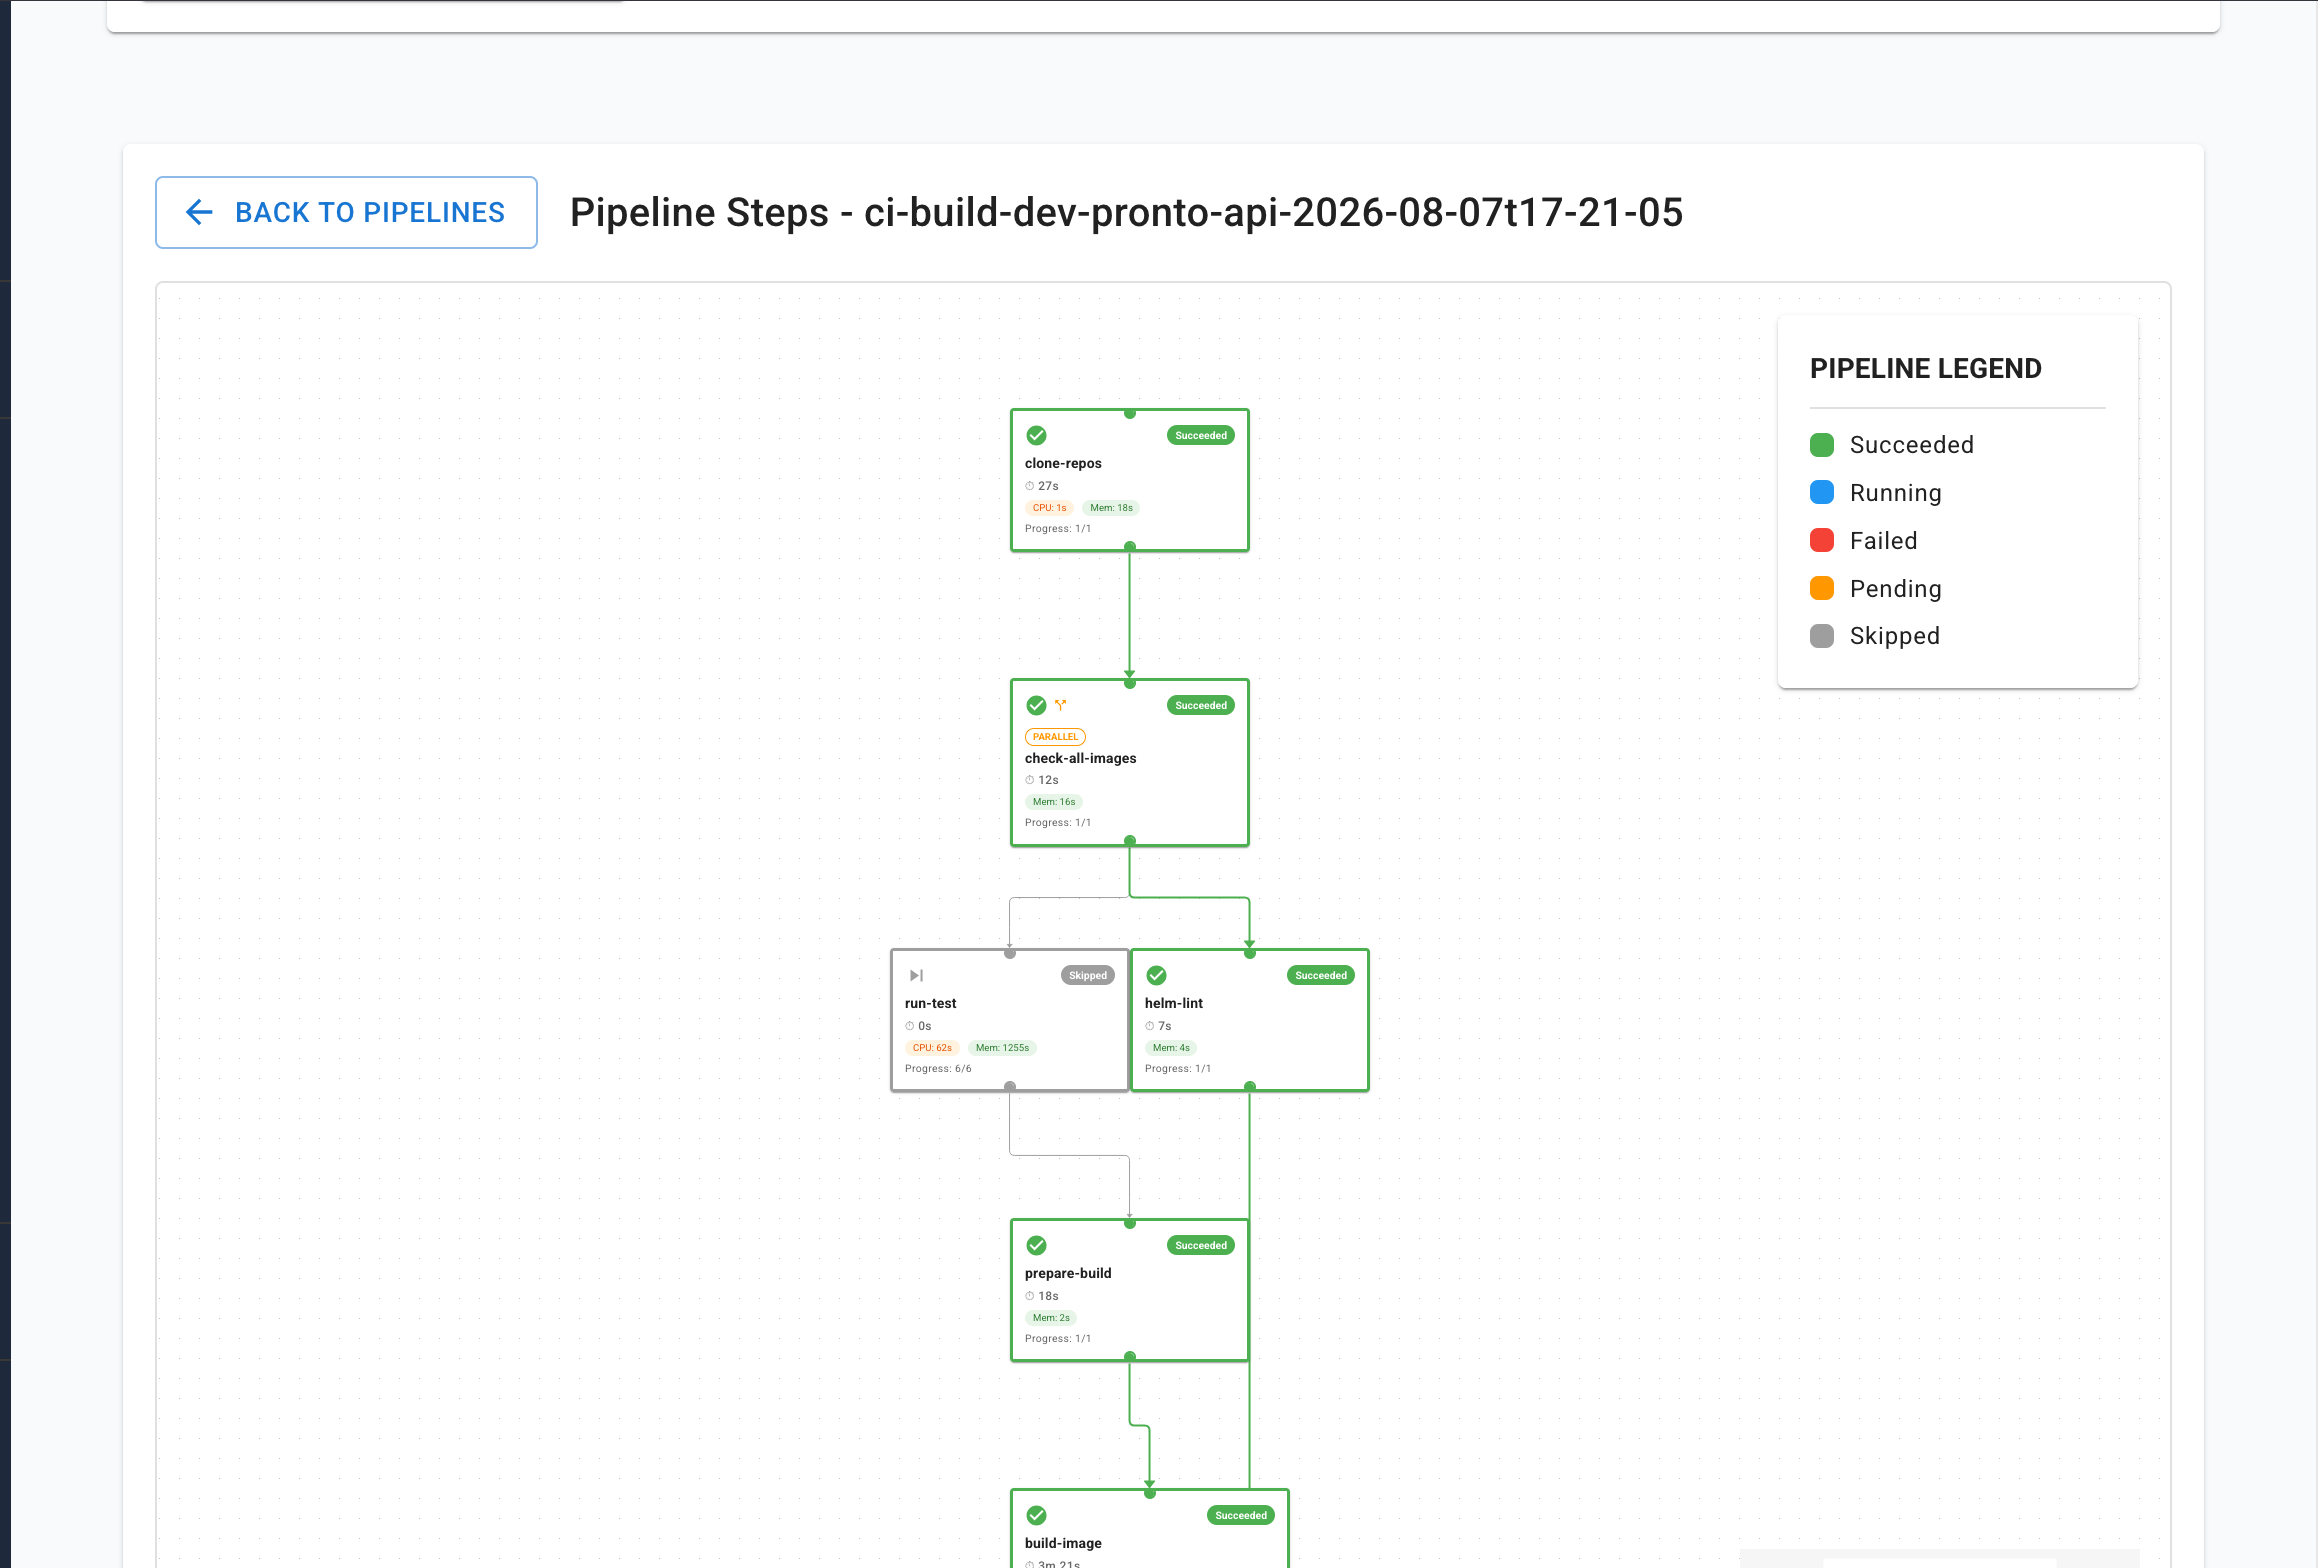
Pipelines you assemble instead of script, test and load runs against any branch, and a security scan on every image.
Release
Releases the right people can approve
Scope from your tickets, an approval at each gate and a GitOps rollout — for Kubernetes services, frontends and Shopify alike.
Infrastructure & operations
Cloud infrastructure from a form, reviewed before it runs
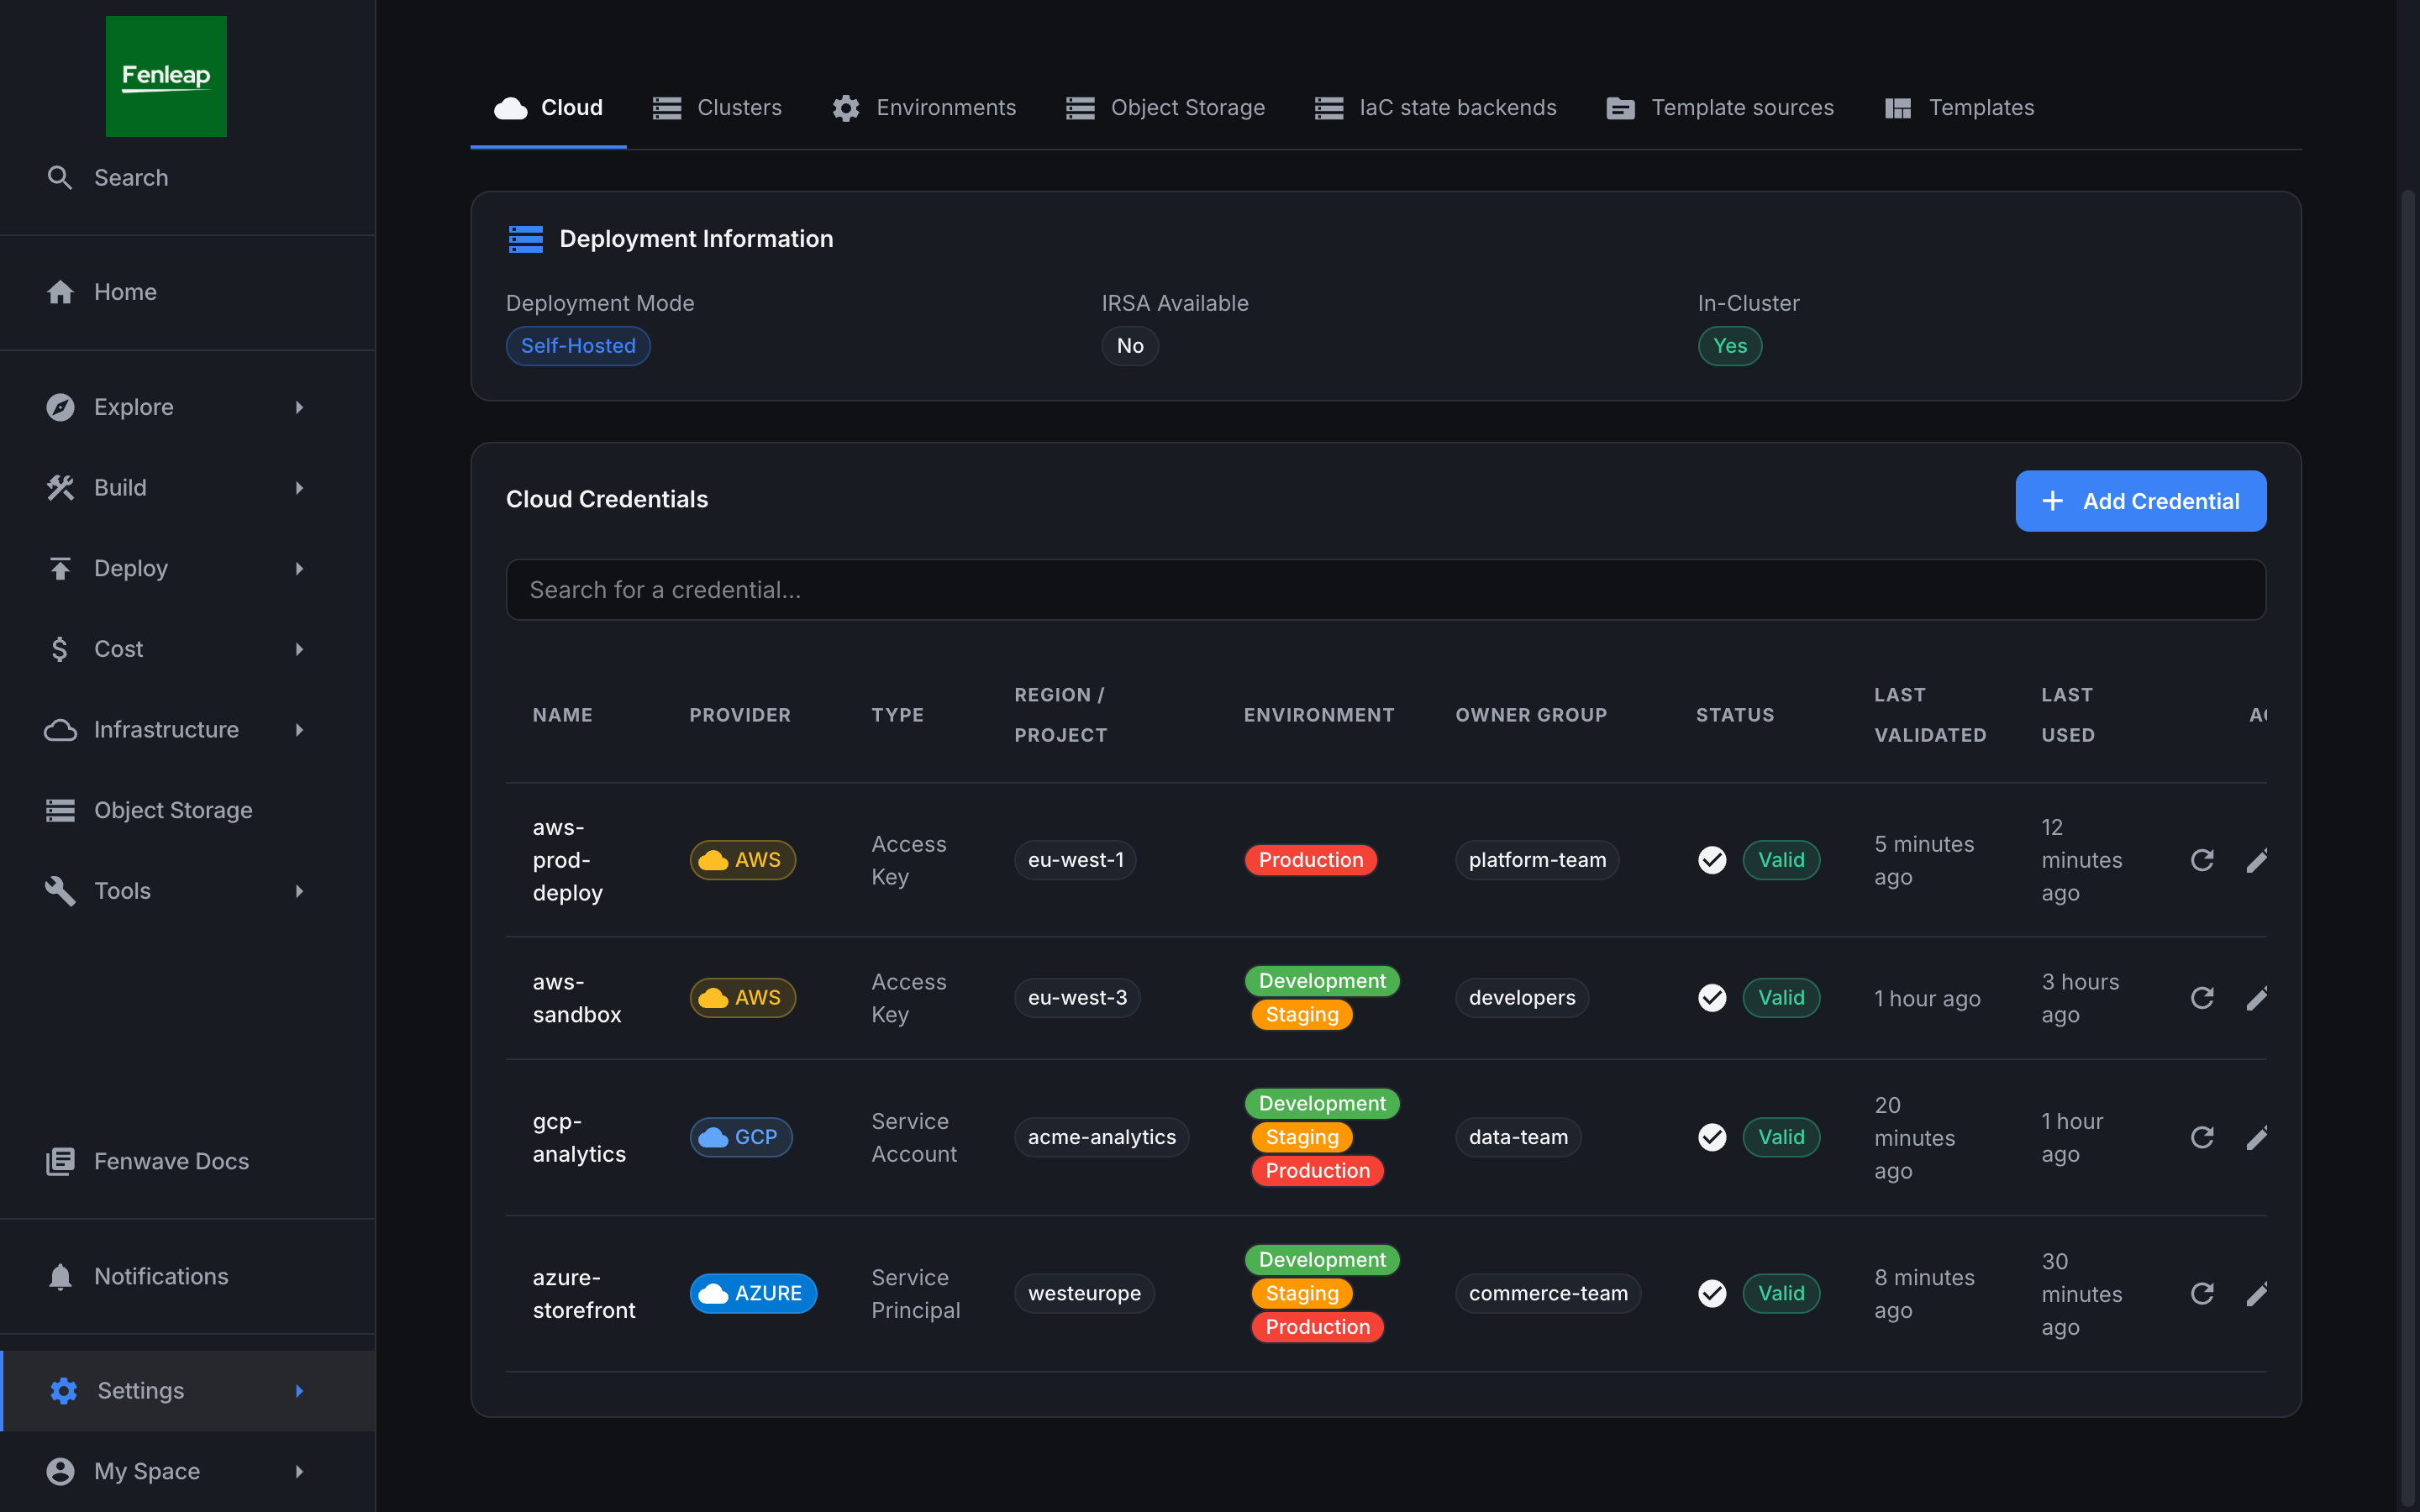
Terraform, OpenTofu and Pulumi on AWS, Google Cloud and Azure, with the plan reviewed before anything changes. Then the clusters, buckets and costs that follow, in one place.
Catalog & docs
Know what runs, and who owns it
Every service with its owner, its documentation and what it depends on. One place to search instead of a wiki per team.
Govern & connect
Your tools, your rules
Access scoped to each role, every action logged and cloud keys never handed out — connected to the tools your teams already use.
See Fenwave on your own projects
Thirty minutes, on your repositories and your clusters. We will point out three requests your platform team would stop receiving as soon as next week.