
Security Scanner
Find the secret in the commit, not in the breach report
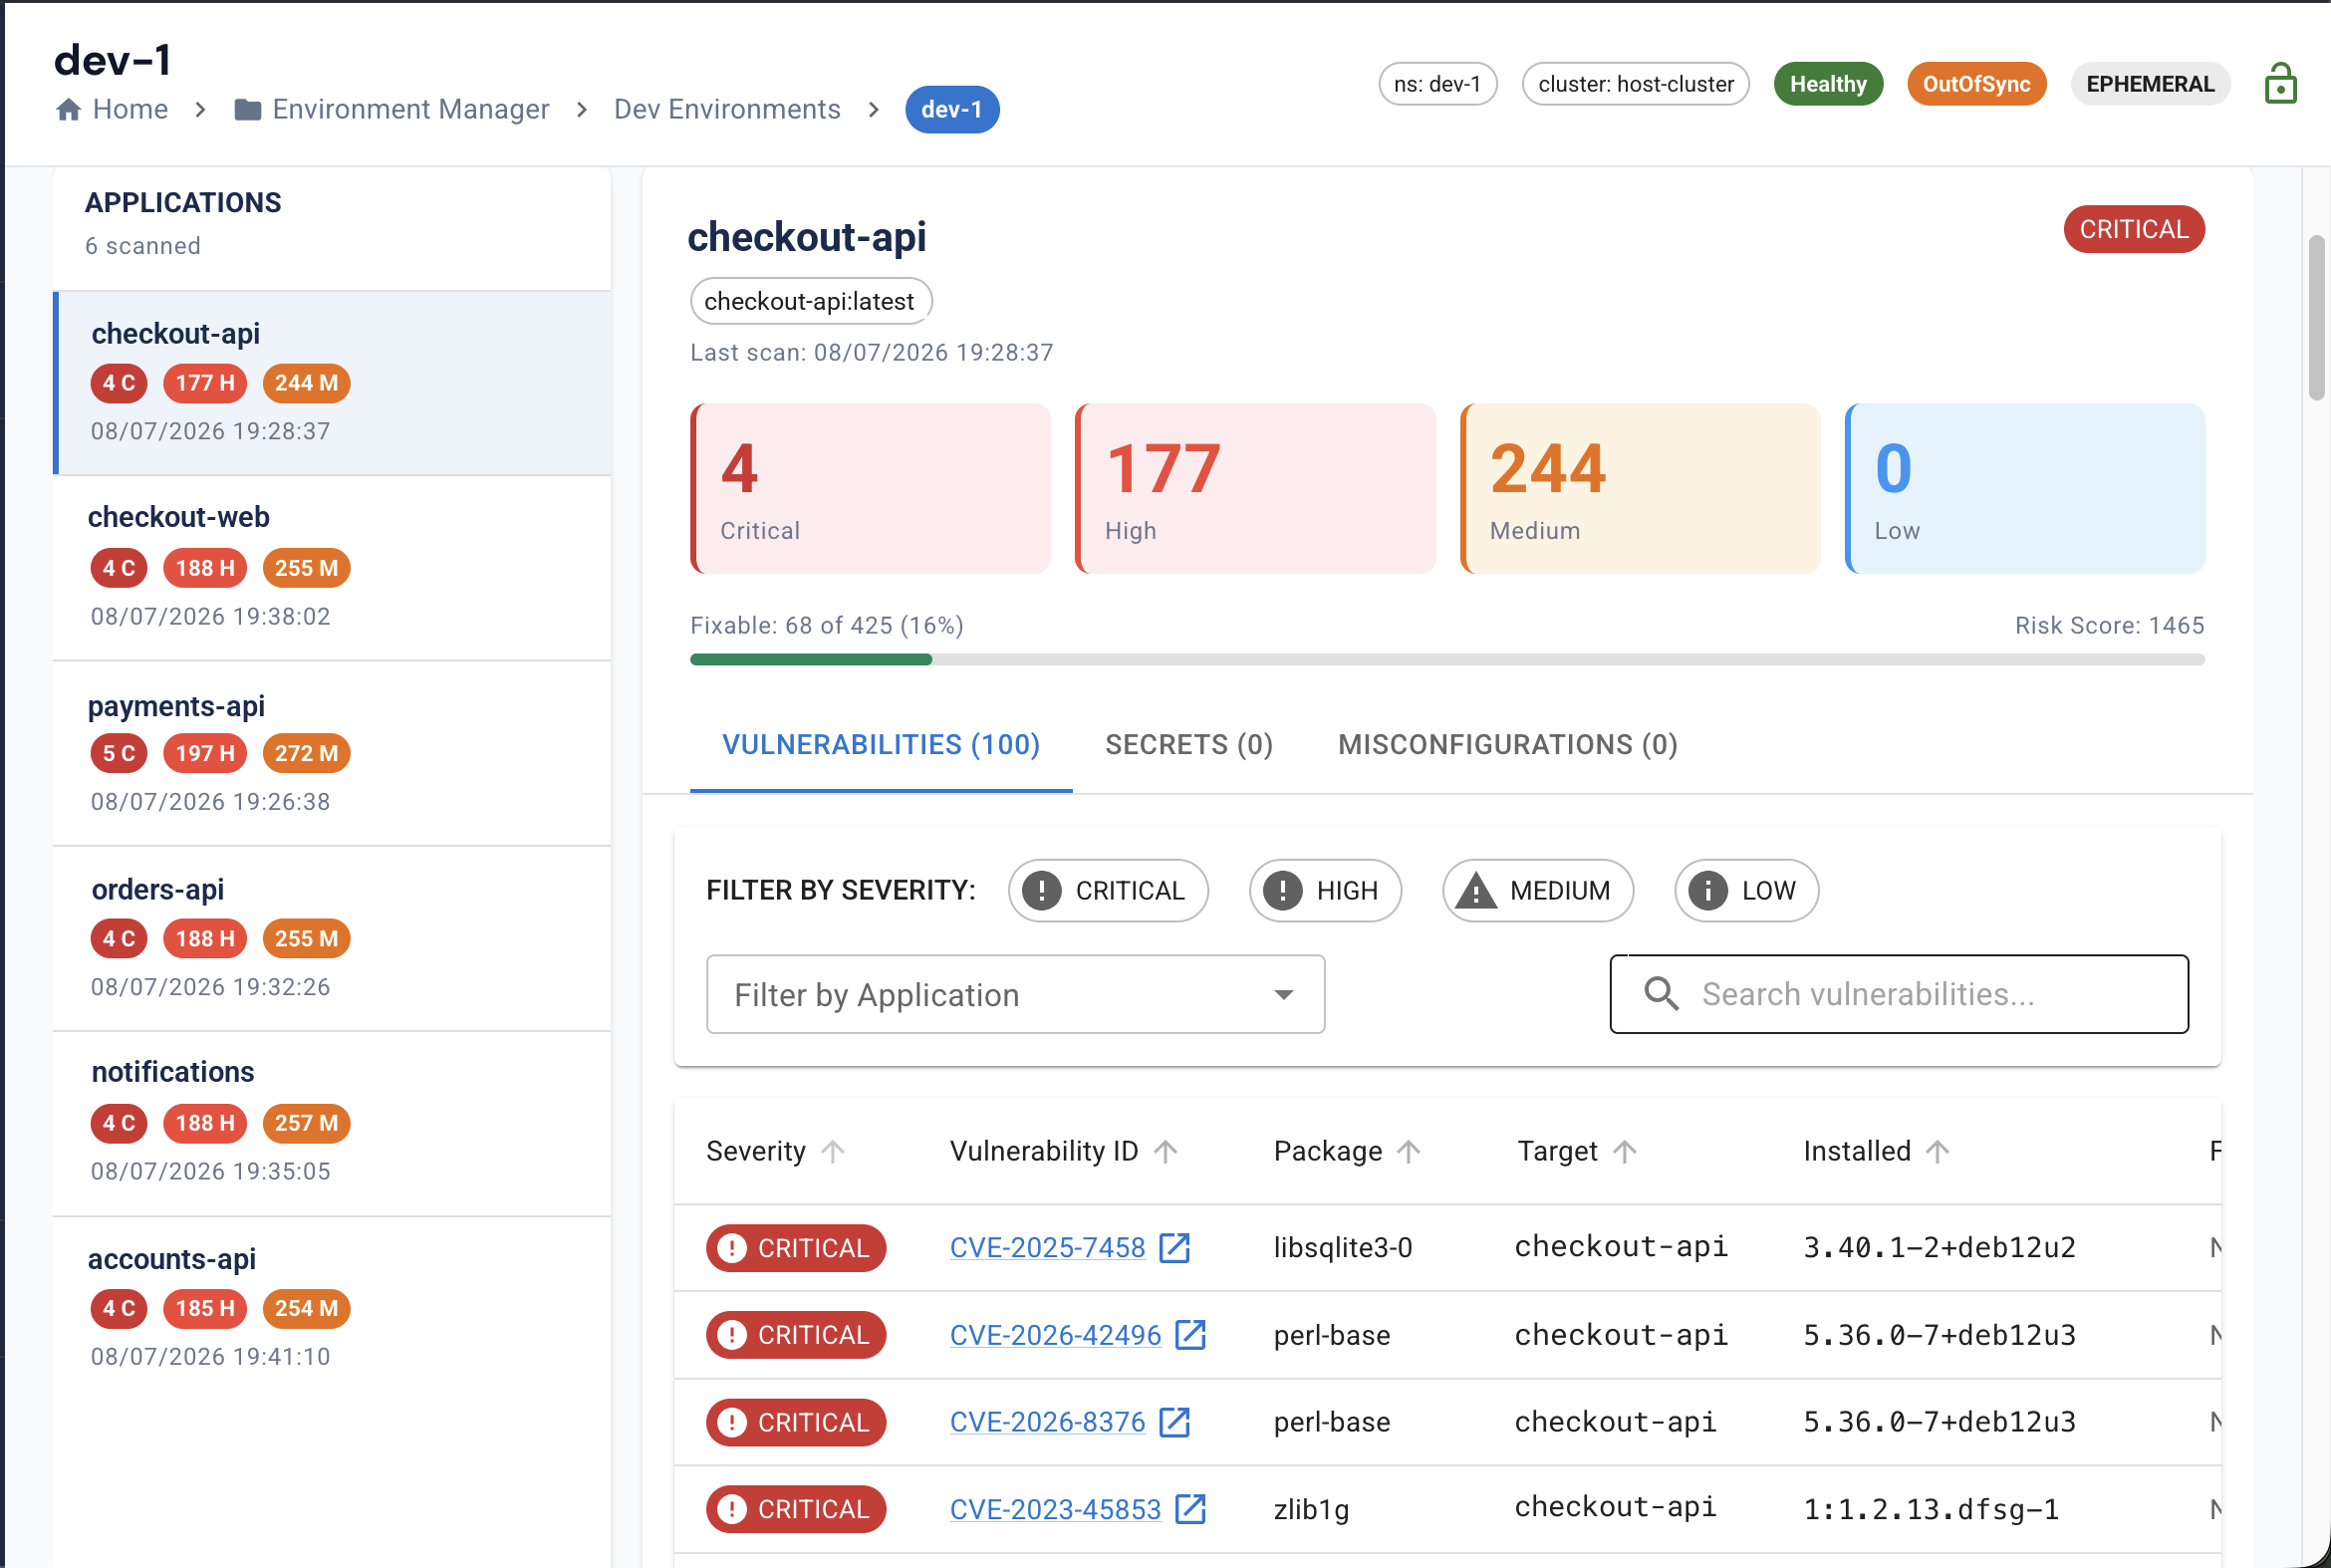
Static analysis, dependency scanning, container scanning and secret detection run against your components on the same screen, with results ranked by severity. It is the scan that runs because it is one click away, not the one scheduled for next quarter.
In this capability
- SAST for source, plus dependency and container image scanning
- Secret detection across history, not just the current tree
- Results ranked by severity with a clear required action
- Integrates SonarQube, Trivy, Snyk and GitLeaks
In Fenwave
Tools›Security Scanner›Run scan
Built on
- SonarQube
- Trivy
- Snyk
- GitLeaks
Where teams use it
More in Build & test
- Pipeline BuilderBuild CI/CD visually, ship it as real YAML
- Test Runner & Stress TestingRun the suite against a branch, keep the evidence
See Fenwave on your own projects
Thirty minutes, on your repositories and your clusters. We will point out three requests your platform team would stop receiving as soon as next week.