
Platform Settings
Grant the access, not the credentials
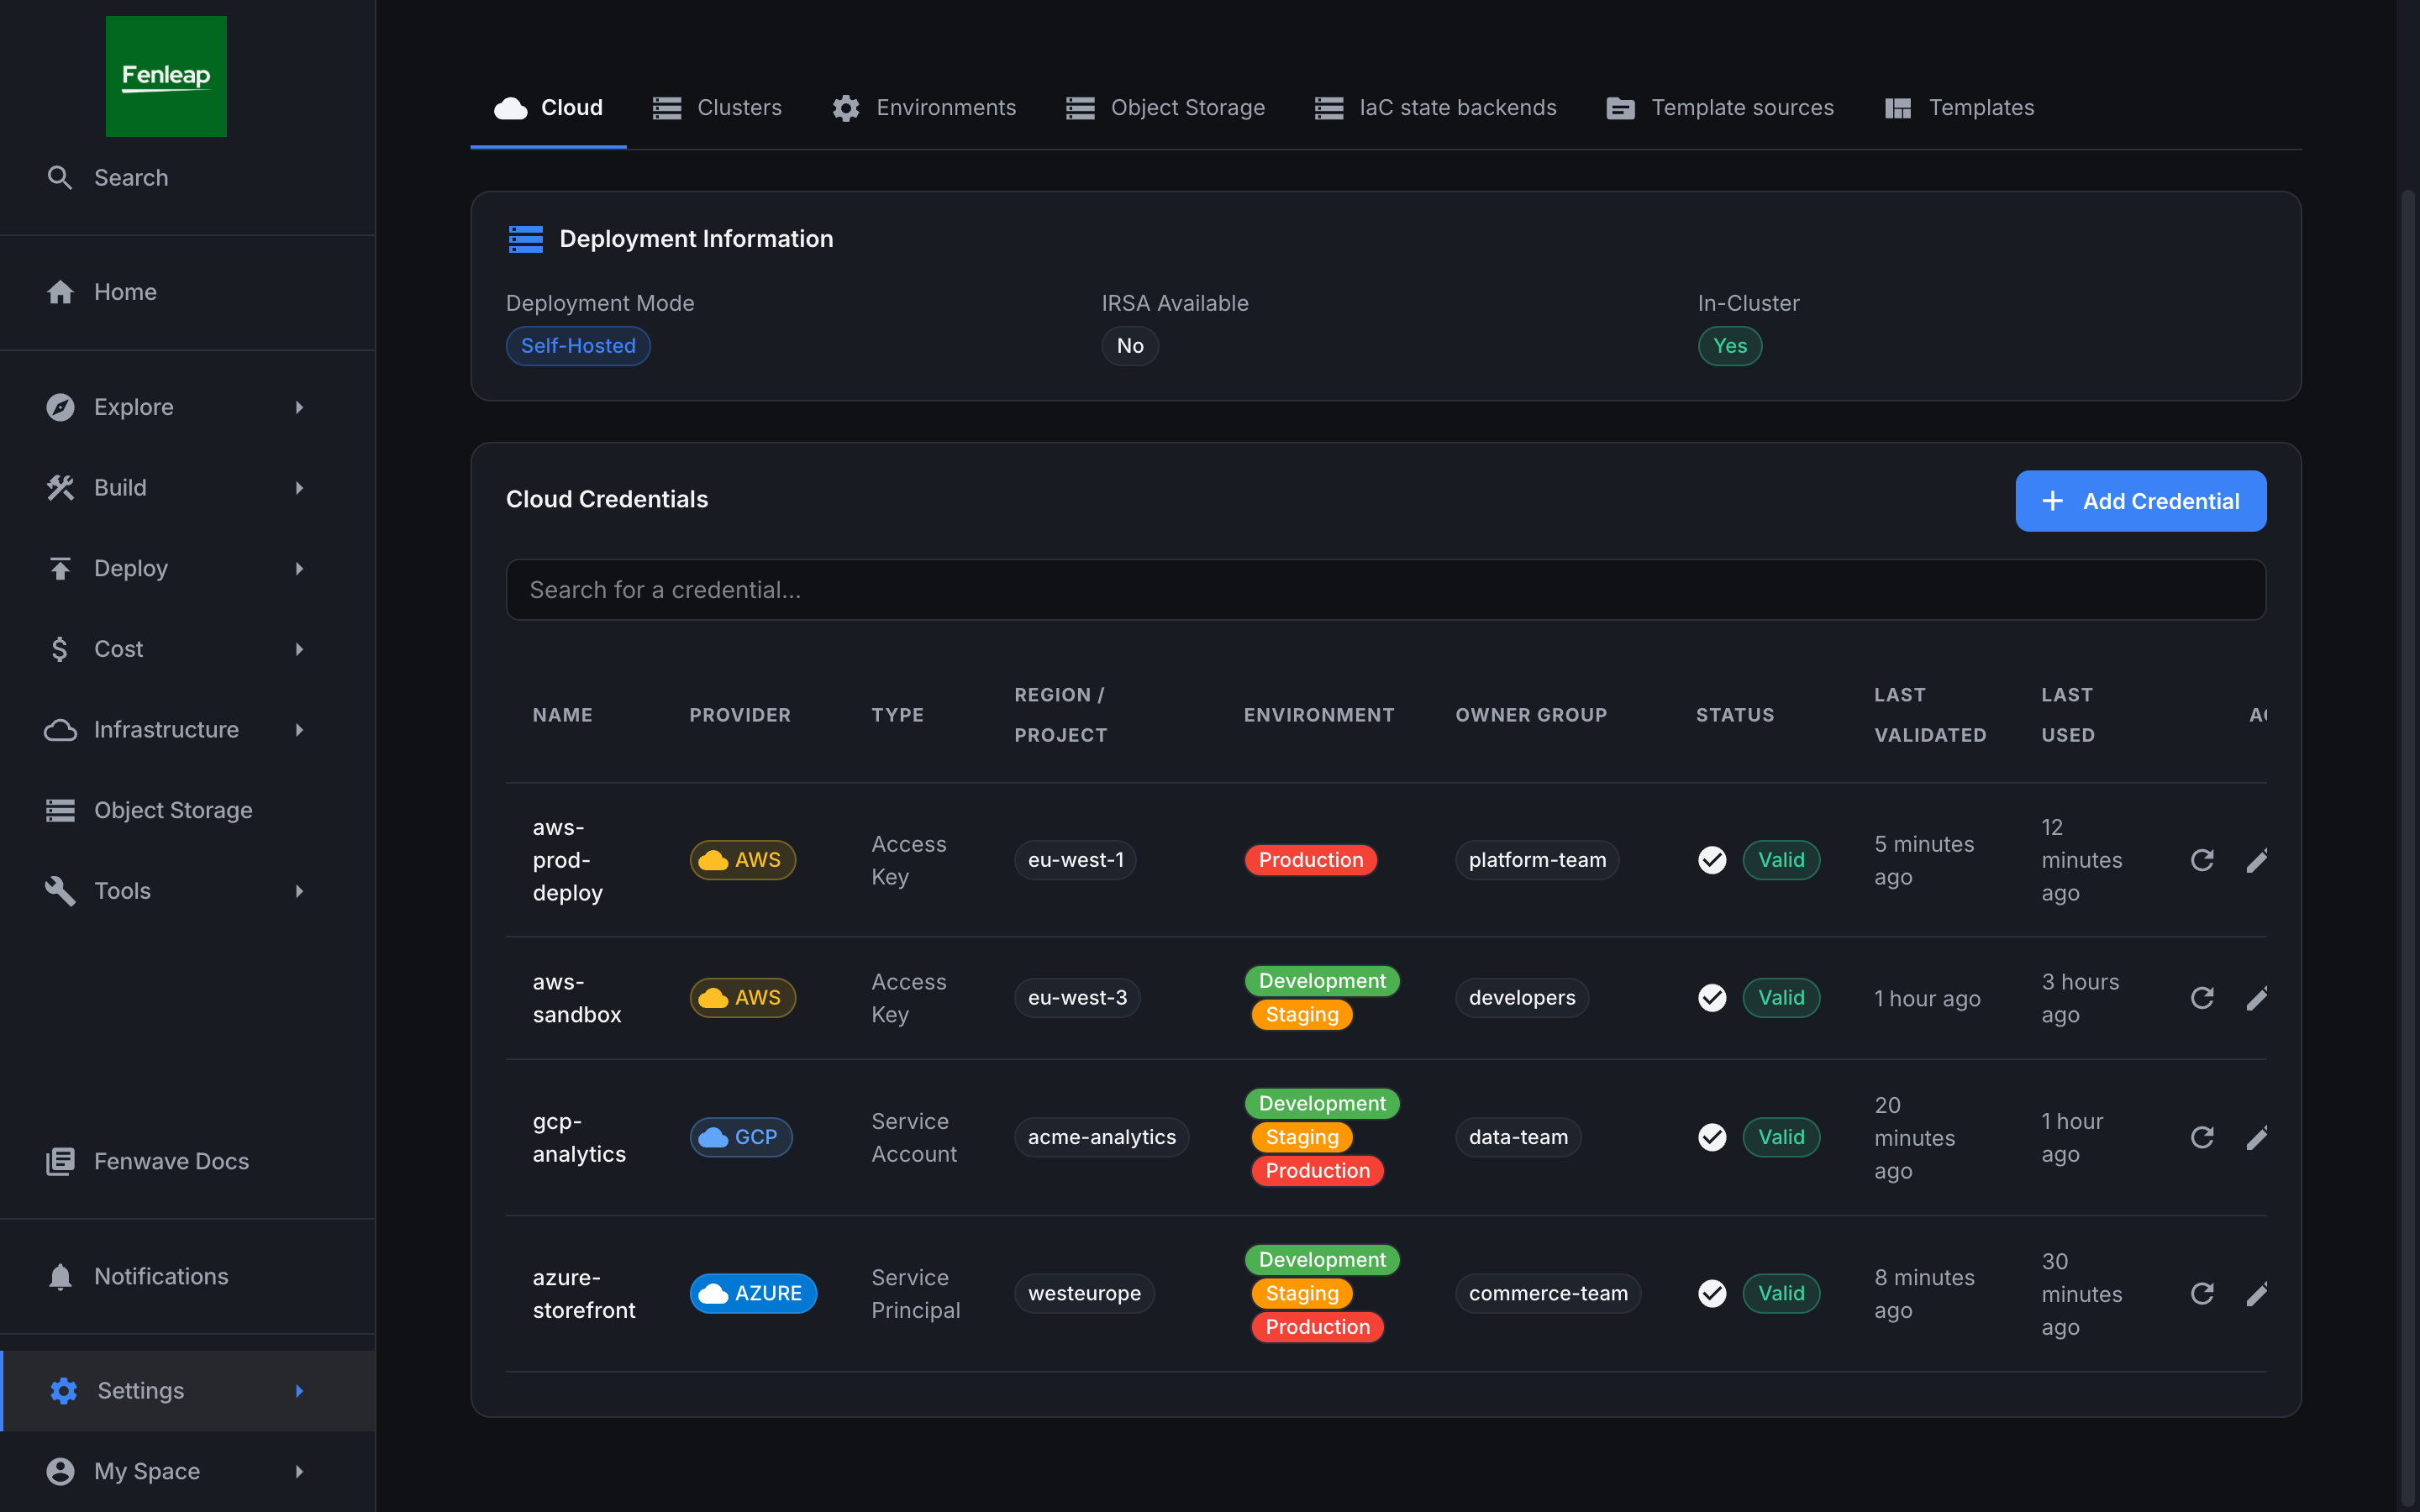
Roles, groups, clusters, repositories, cloud credentials and storage connections are configured in one place. Cloud keys are stored once by an administrator and never handed out; a person is granted a scoped role instead, which is what makes it safe to give a marketing manager a bucket.
In this capability
- Granular RBAC down to a single storage connection or environment
- Cloud credentials for AWS, GCP and Azure stored once, never shared — static keys, workload identity or managed identity
- Register clusters, repositories and environment types centrally
- Groups mapped from your identity provider
- Audit trail attributing every privileged action to a person
In Fenwave
Platform Settings›Users & permissions›Roles
Built on
- OIDC
- SAML
- Backstage Permissions
Where teams use it
More in Govern & connect
All featuresSee Fenwave on your own projects
Thirty minutes, on your repositories and your clusters. We will point out three requests your platform team would stop receiving as soon as next week.